Broadcom has shipped patches for 89 newly discovered vulnerabilities in TrueSource Spring Enterprise, delivering them early to critical infrastructure customers and other qualifying organizations ahead of public disclosure. The release brings the cumulative count of vulnerabilities fixed across the TrueSource portfolio to 408, as the company continues a security push it began earlier this year.
Closing the gap between patch and deployment
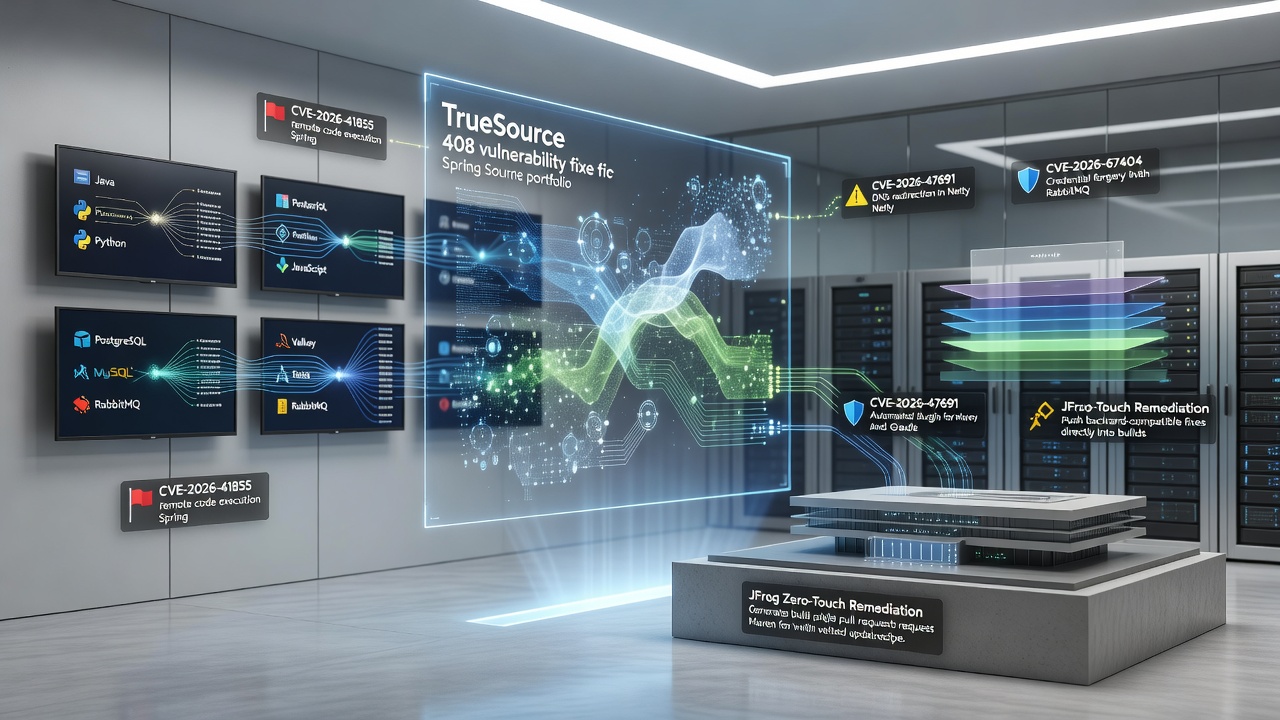
Issuing a fix is only half the job; it has to reach production code before it protects anything. To address that gap, Broadcom is adding TrueSource Hub, a tool that connects to an organization's code repositories and shows which applications depend on which open source components - spanning Java, Python, and JavaScript libraries, container images, and data services. Rather than a one-time audit, Hub offers a live view of exposure and patch status, letting security teams prioritize fixes based on which applications carry the most risk.
Build plugins for Spring Application Advisor extend that automation into everyday development work. The plugins integrate directly with Maven and Gradle, generating pull requests built on vetted update recipes so engineering teams can review and merge fixes without manually tracking down affected dependencies. A new integration with JFrog Zero-Touch Remediation goes a step further, pushing verified, backward-compatible fixes directly into builds without waiting for a manual pull request.
Scope of the fixes and how patching works
Broadcom says it fixed 406 new vulnerabilities in Spring and Reactor libraries during 2026 alone, delivering more than 1,090 total fixes, including 798 backports, after reviewing over 2,600 vulnerability reports and filtering out more than 3,000 false alarms. TrueSource Spring Enterprise applies fixes simultaneously across every supported version, so organizations running older releases get the same protection as those on current versions, without needing to upgrade first. Security-only patches - isolated from unrelated feature changes - are meant to speed up deployment and review.
Earlier fixes this year addressed a remote code execution flaw in Spring (CVE-2026-41855), a maximum-severity DNS redirection issue in the Netty dependency (CVE-2026-47691), and a credential forgery vulnerability in RabbitMQ (CVE-2026-67404). Broadcom says detailed vulnerability information for the newest batch will be published once fixes reach the broader community and CVE identifiers are issued.
Part of a broader enterprise open source strategy
TrueSource Spring Enterprise is one of three offerings under Broadcom's TrueSource portfolio, alongside Trusted Artifacts, covering verified libraries and container images, and Data Services, which supports engines such as PostgreSQL, MySQL, Valkey, and RabbitMQ. Broadcom also says it is working with vulnerability-scanning vendors, including Snyk, so that components already patched through TrueSource are recognized as resolved rather than continuing to trigger alerts. TrueSource Spring Enterprise, Hub, and the build plugins are generally available now through tiered site licensing, with the newly fixed vulnerabilities available immediately to early-access and critical infrastructure customers ahead of public CVE disclosure.